
If you have not yet updated your iPhone to the latest version of iOS, our editorial team strongly recommends that you do so. On October 15, Maria Dorvey had $16,000 in crypto stolen from several different wallets, on an iPhone 15 running iOS 18.
How It Happened
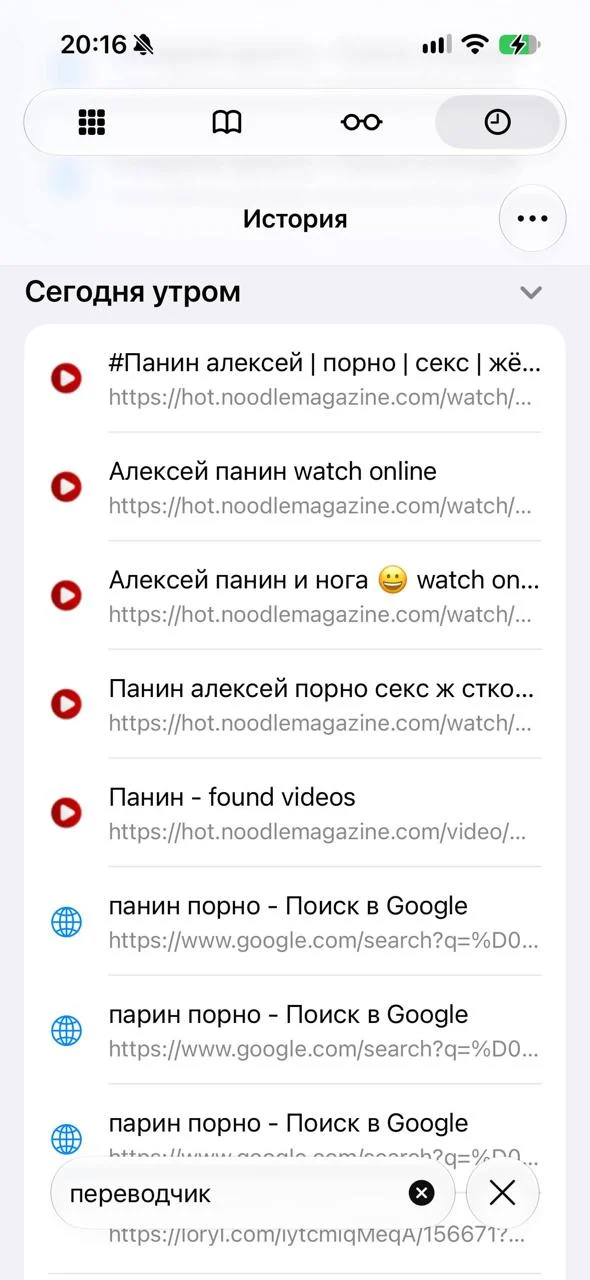
Morning of October 15, Maldives. Maria is lying on the beach, with her iPhone 15 on iOS 18 nearby, using mobile data with no Wi-Fi at all. Around noon, she searches Google for an interesting video with Panin and opens it in Safari. One ill-fated tap on an ad, and a redirect to an unfamiliar domain flashes by. Nothing is downloaded, nothing is installed, and there is not a single permission prompt.
At 12:29:48, 16,428 USDT leave her Tron wallet. Twelve seconds later, TRX follows, leaving exactly 0.04 in the account. The thief script left the same balance in half of the drained wallets. At the same time, wallets on the TON network are emptied. Three apps with three different seed phrases are drained at once, and Maria had never written down two of those phrases anywhere.
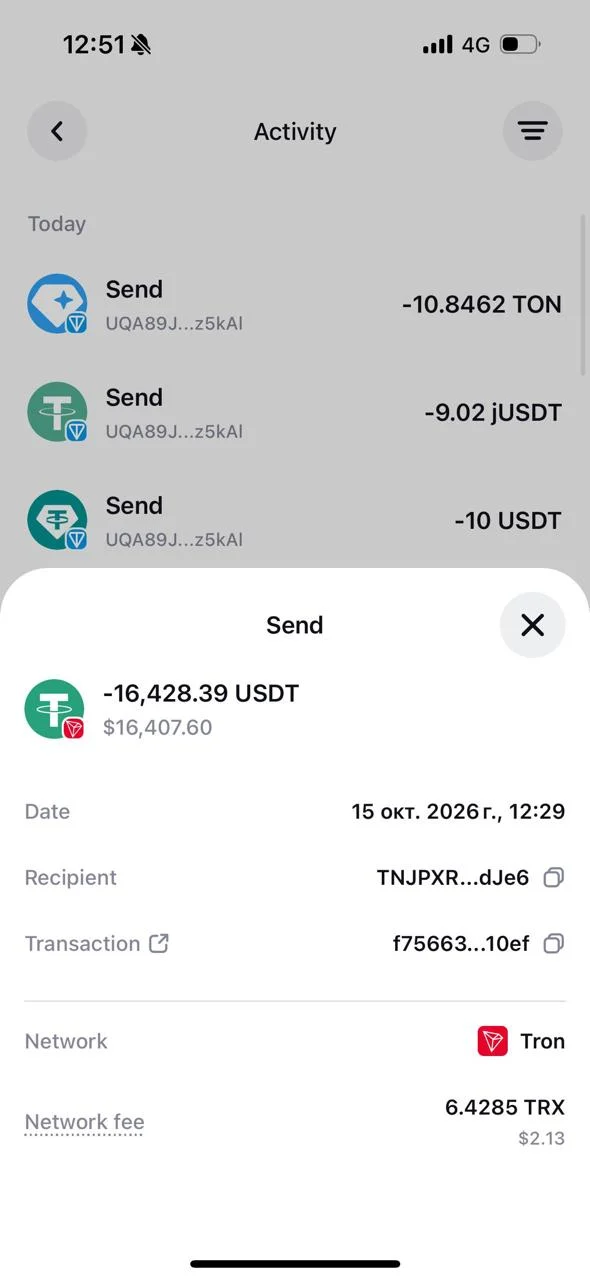
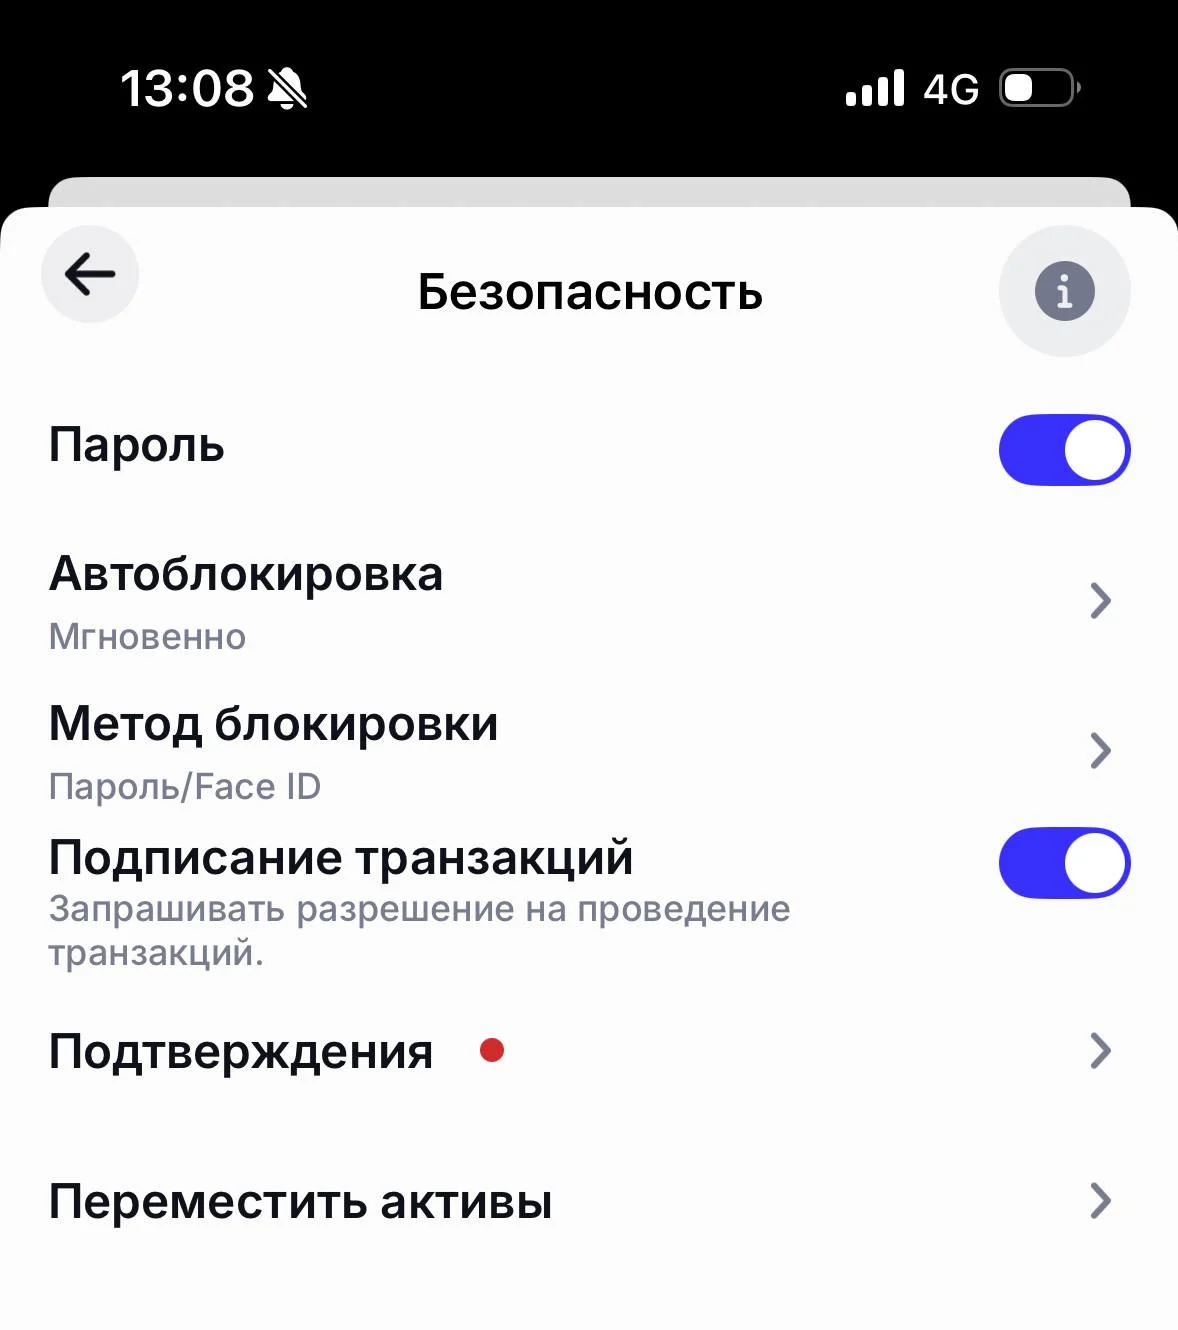
“Transaction signing” is enabled, but the transactions are no longer being signed by her phone, they are being signed by someone else’s computer using her keys.
At 12:51, she gets out of the water and opens the wallet history. She sees a collector wallet that already contains money from sixteen other wallets, totaling $174,000. At 13:50, the entire amount is converted into USDD, which Tether cannot freeze.
Then the phone becomes a “brick”: apps disappear, and the banking app will not open. Maria buys a ticket home and sums it up: “Panin porn has never cost me 1 million before.” That evening, the collector takes another $10 from yet another stranger.
What Was It?
When she visited the site with the Panin video through Safari on iOS 18, she most likely got hit with an exploit in the DarkSword mold: it works on iOS 18.4-18.7 and infects an iPhone after a single page opening in Safari, with no downloads, extra clicks, or confirmations. In this case, it could have been an ad redirect from the site where she watched the Panin video. Such an exploit obtains wallet data and seed phrases within minutes, and the attacker then signs transfers on their own device. This is why “Transaction Signing” did not help: it only protects actions inside the app on her phone.
Crypto Flow Scheme
More Cases
Maria’s case is not the only one, here are several more incidents involving the same exploit.
Case No. 1
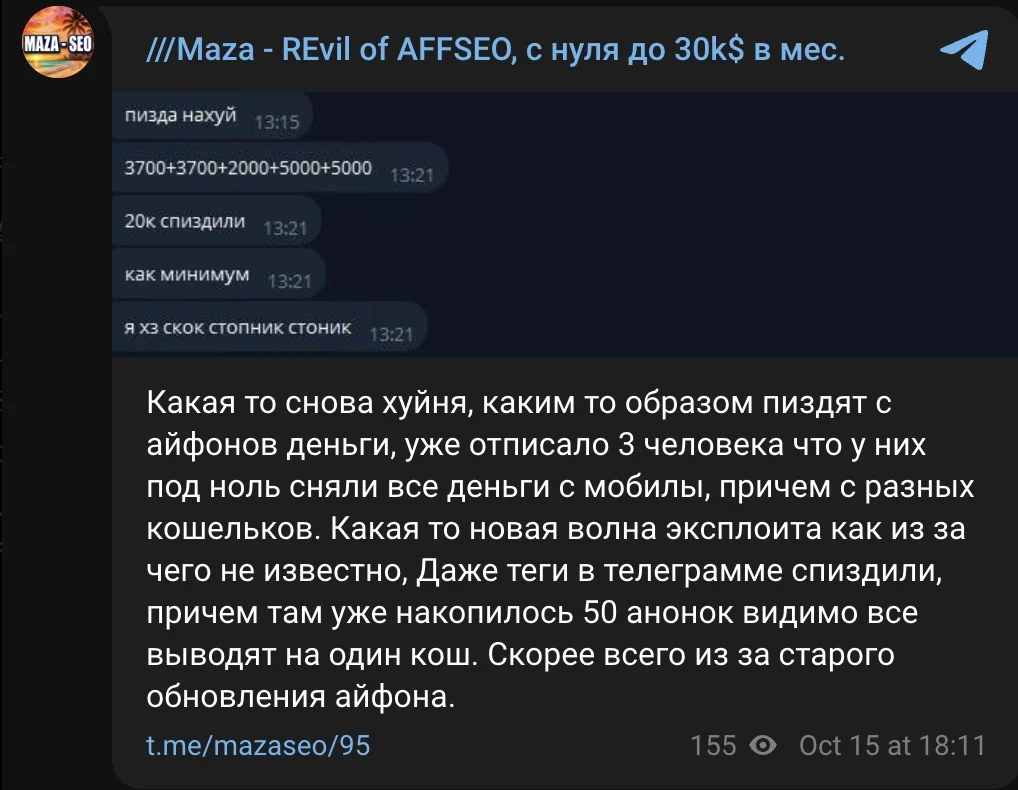
A post in the @mazaseo channel. Three iPhone owners messaged the author after all their funds were debited on the same day, from different wallets.
Case No. 2
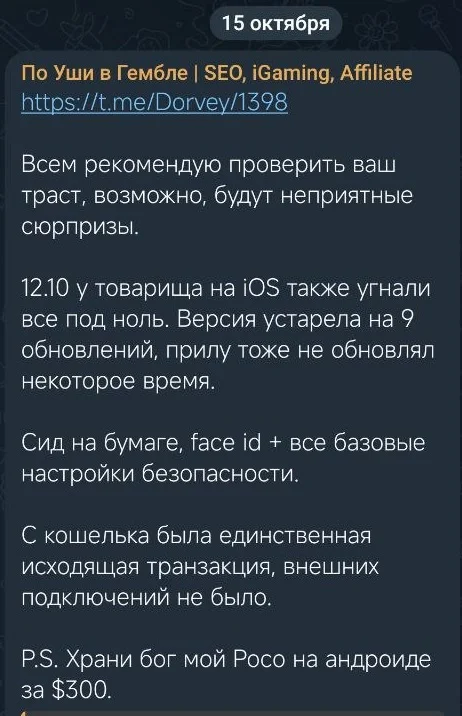
On October 12, funds were debited from a wallet on an iPhone whose iOS was nine updates behind. The seed phrase was stored only on paper, and there was one outgoing transaction. A post in the “По Уши в Гембле” channel.
Comments